The work behind
the intelligence.
Investigations, campaign tracking, technical research and practical defensive engineering. First-hand work from the team @ Lab539.
[AnyDesk TAG] AnyDesk and ScreenConnect in a campaign targeting banking customers
An investigation into bank-themed fraud sites, signed malware, AnyDesk and unattended ScreenConnect access.
Read research
Pre-Attack Indicators
Why intelligence discovered during adversary preparation deserves to be recognised and acted on.
Read research
FulcrumSec - A look at their tradecraft
The tradecraft behind FulcrumSec’s campaigns, exposed credentials and cloud access.
Read research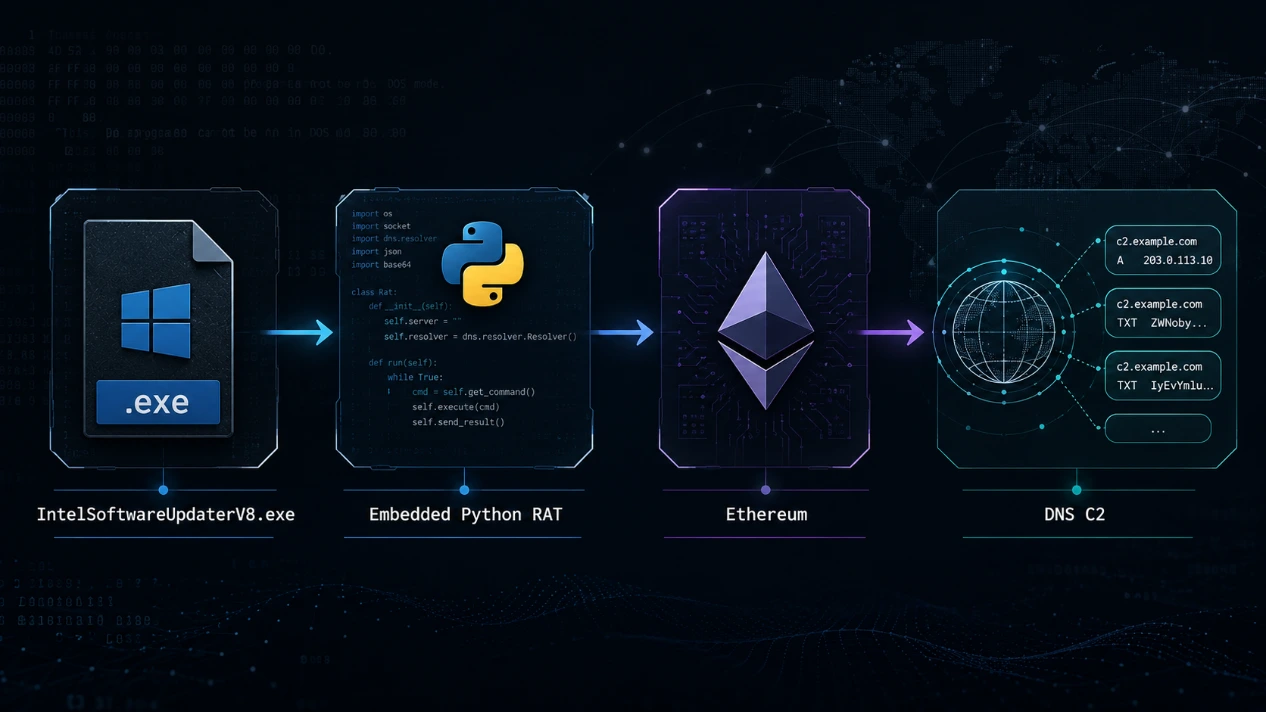
From Ethereum to DNS C2: Reverse Engineering the ClickFix Payload
Dissecting a ClickFix payload that uses Ethereum for discovery and DNS for command and control.
Read research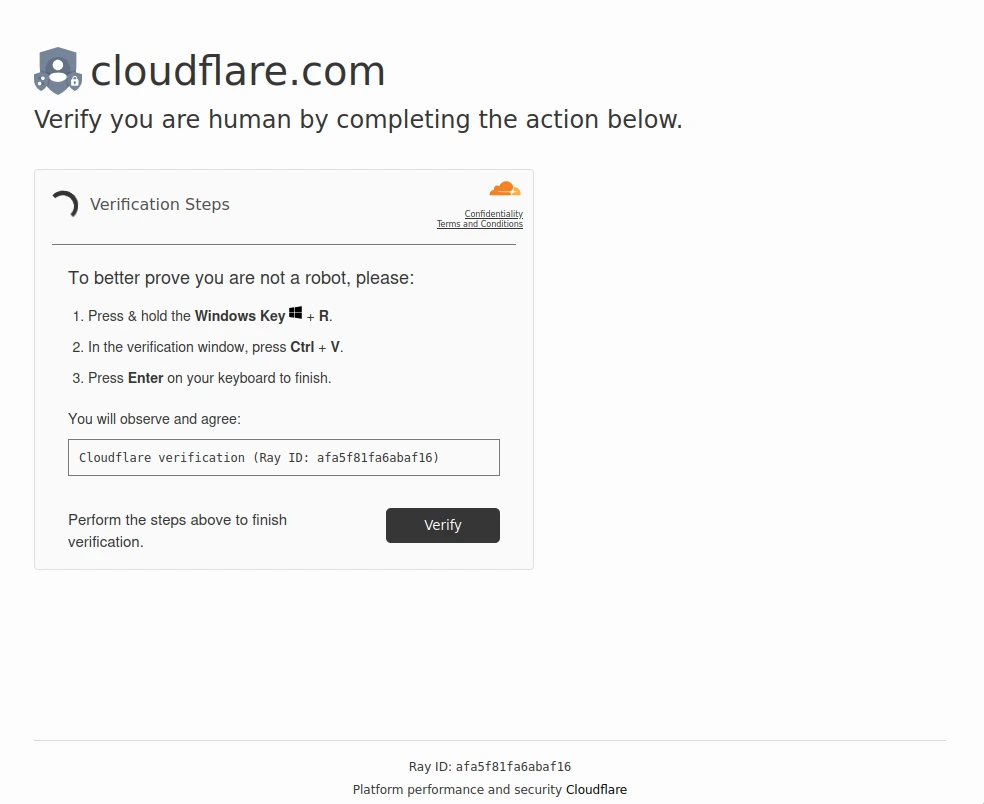
From Compromised WordPress Sites to Blockchain-Backed Malware
Following ClickFix from compromised WordPress sites through blockchain-backed staging to malware.
Read research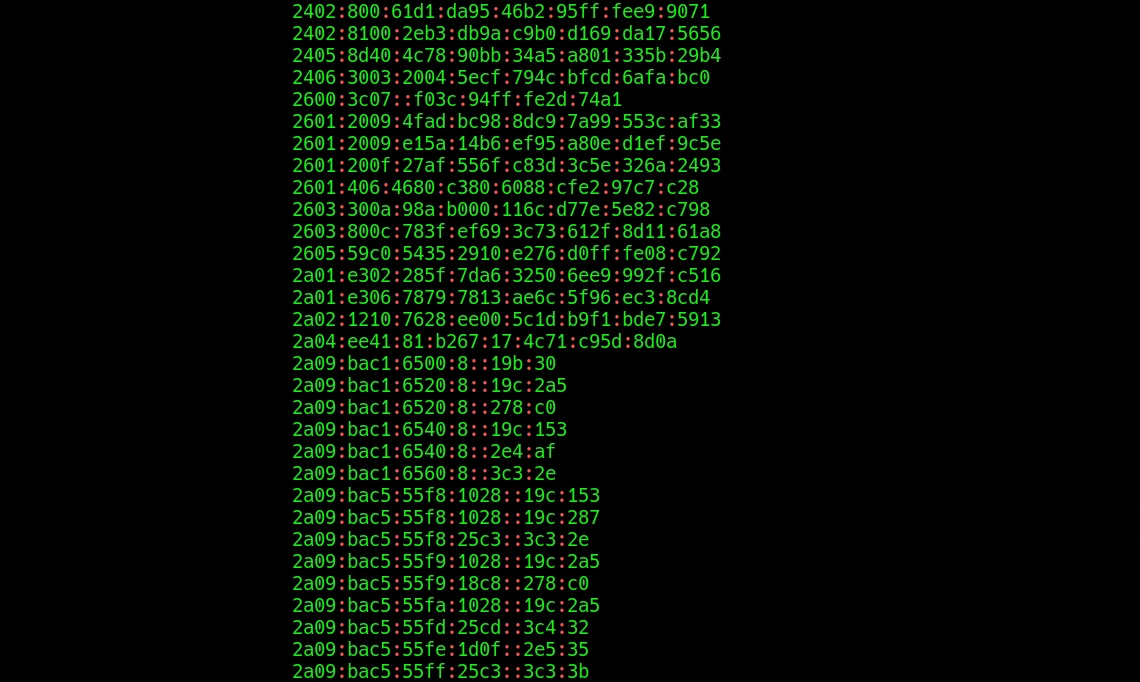
IPv6 Trends in User Account Compromises
The IPv6 address space is changing the economics of account takeover and IP-based blocking.
Read research
What I Learned from Sitting in on a Scattered Spider Sentencing
Technical observations from the sentencing of two prominent Scattered Spider members.
Read research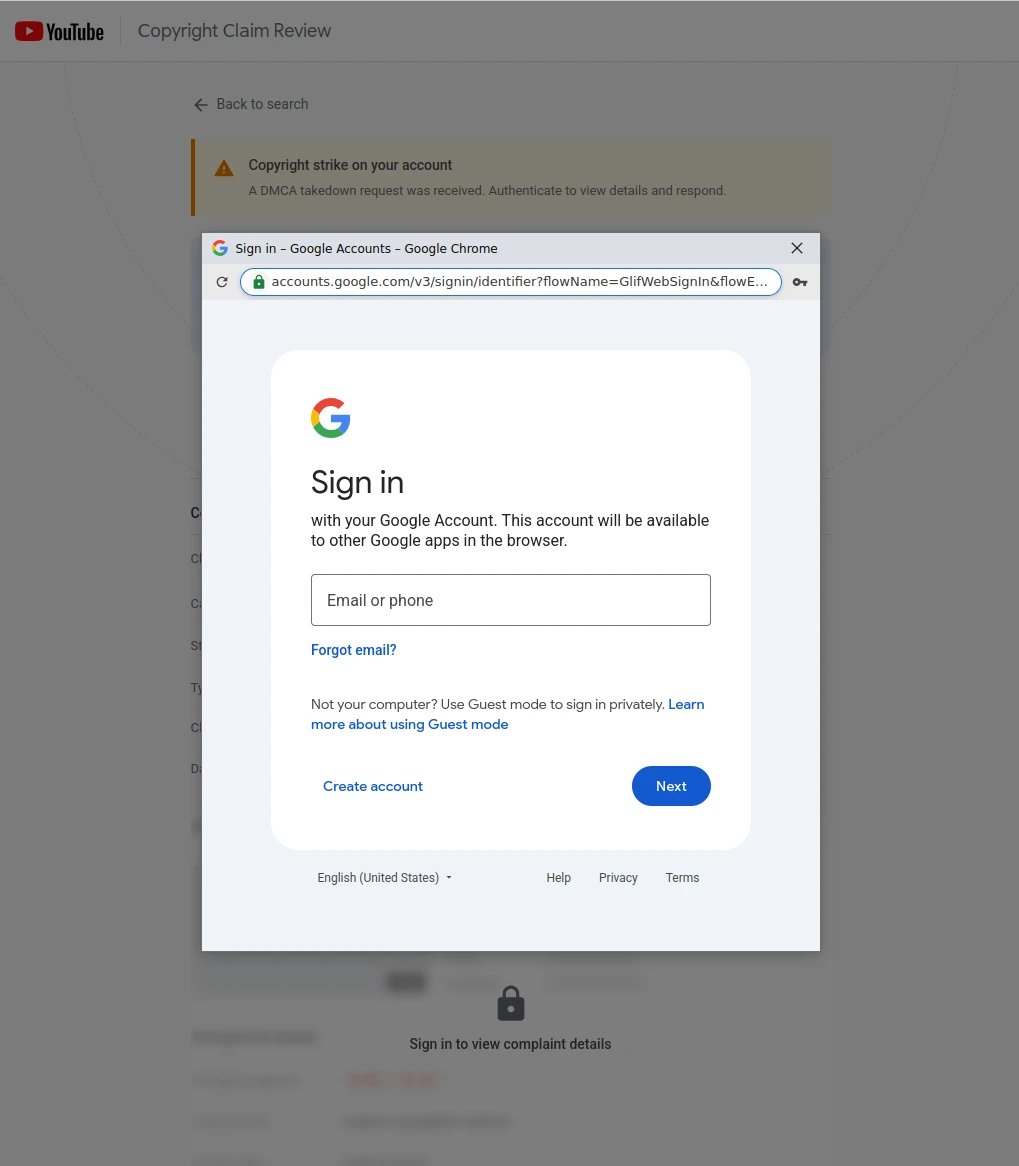
When DMCA Comes Knocking - Part 2: The Sign-in Window That Isn't
A close look at the browser-in-the-browser component of a DMCA-themed phishing kit.
Read research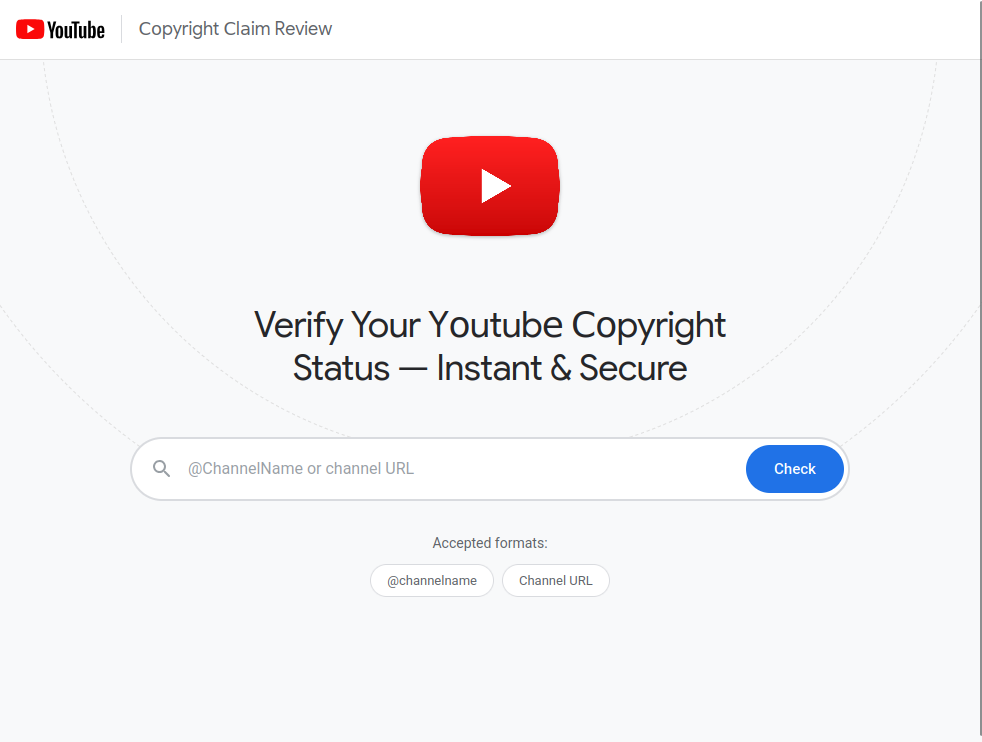
When DMCA Comes Knocking - A YouTube Creator Phishing Kit, Part 1
An investigation into the lures and infrastructure targeting YouTube creators.
Read research
Blob URLs - The Phishing Disguise Hiding in Your Browser
How malicious sites hide phishing content using browser Blob URLs.
Read research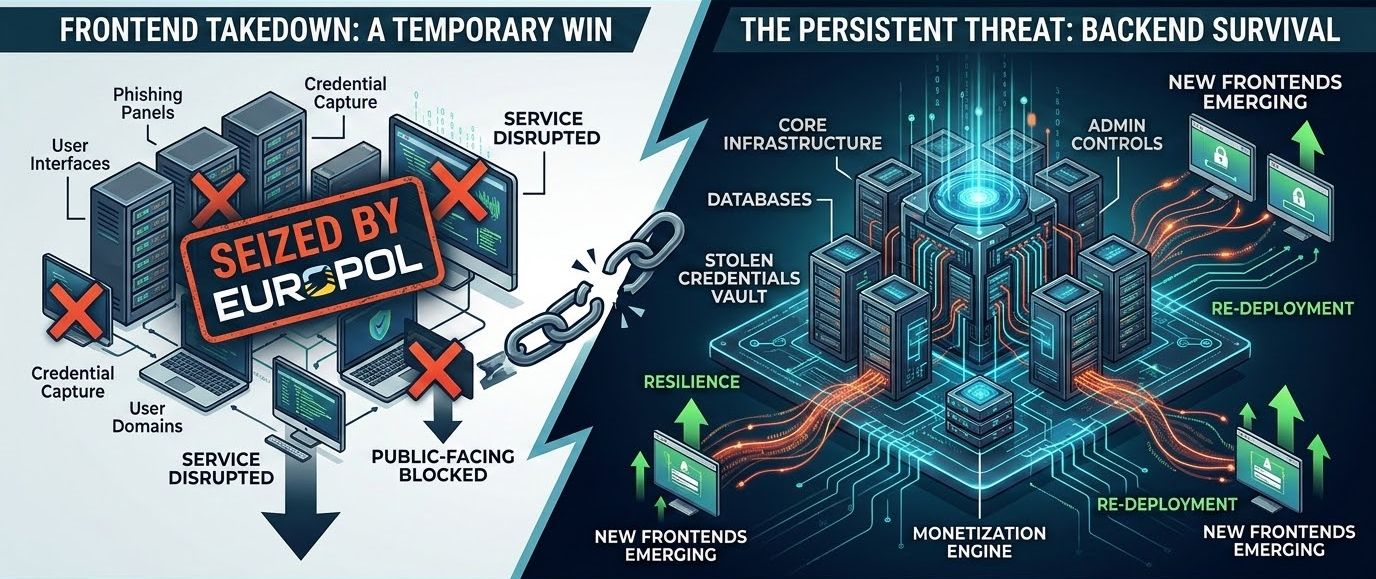
Tycoon2FA is Down - What Happens Next?
The Tycoon2FA takedown and the operational questions it raises for defenders.
Read research
Starkiller - A Reminder That a Residential Proxy Strategy is Needed
Mapping the infrastructure behind Starkiller and the role of residential proxy addresses.
Read research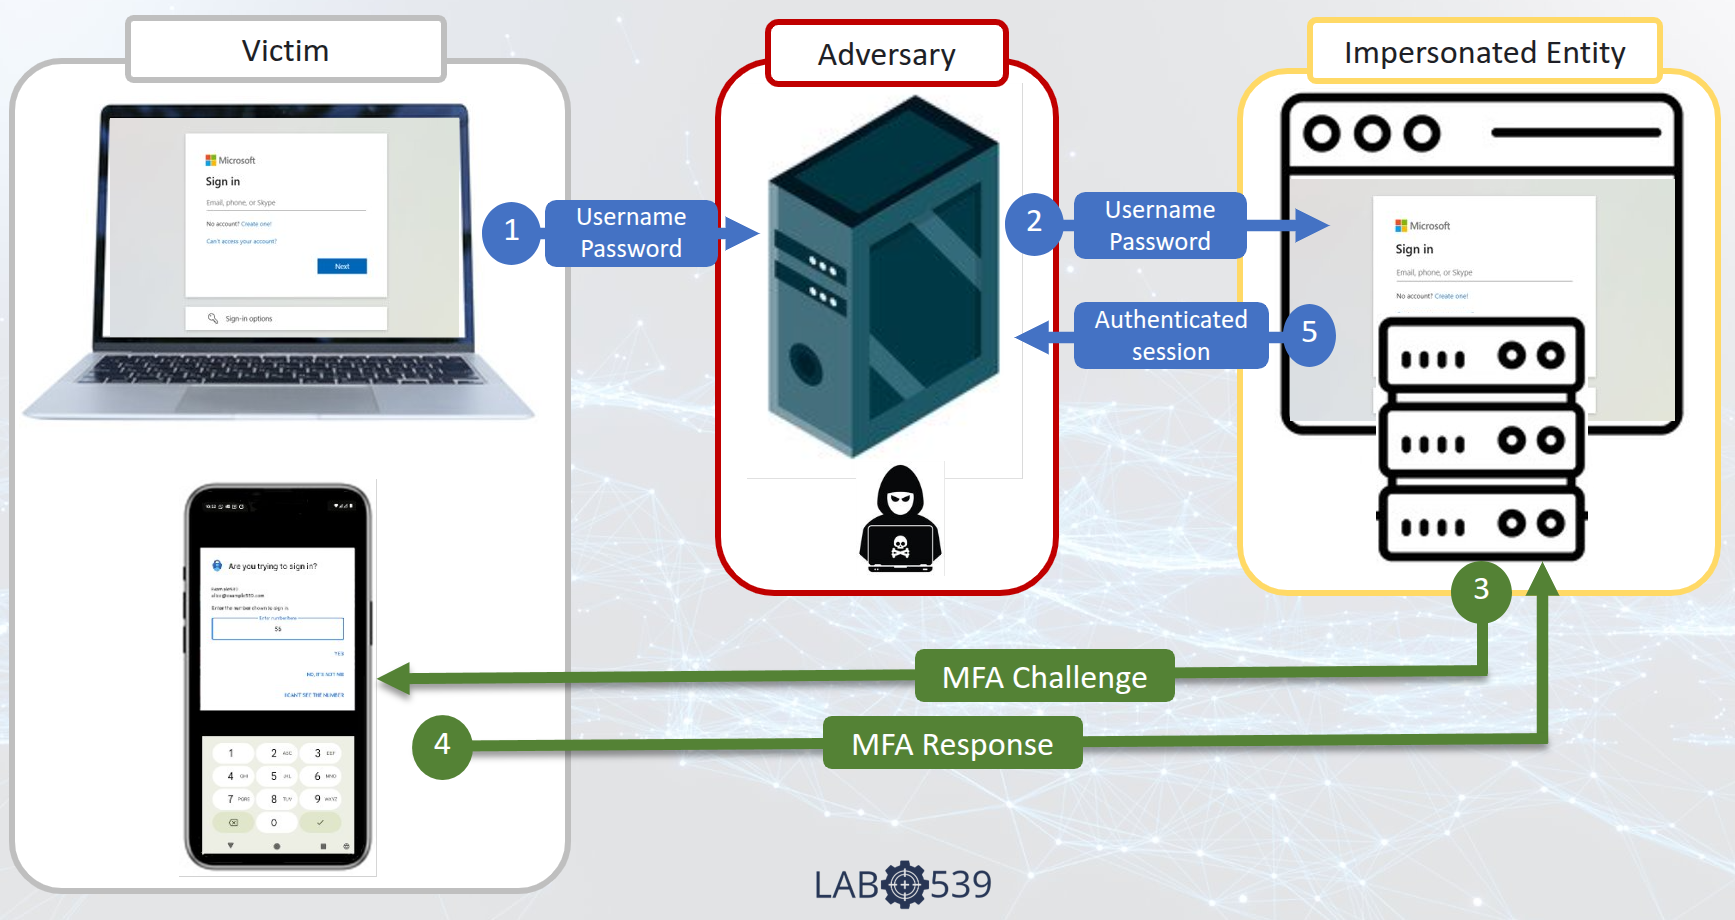
AiTM Detection
Looking beyond reactive alerts to detect adversary-in-the-middle infrastructure.
Read research
Tracking ClickFix Infrastructure
An investigation into ClickFix delivery infrastructure and its overlap with other adversary operations.
Read research
Azure Front Door AiTM Phishing
An AiTM investigation involving infrastructure placed behind Microsoft Azure Front Door.
Read research
Where Conditional Access Risk Policies Fail...
Why certain Microsoft risk-policy configurations can mask successful AiTM attacks.
Read research
AiTM Non-Incident Report
A real attempted AiTM compromise stopped by preventative Conditional Access controls.
Read research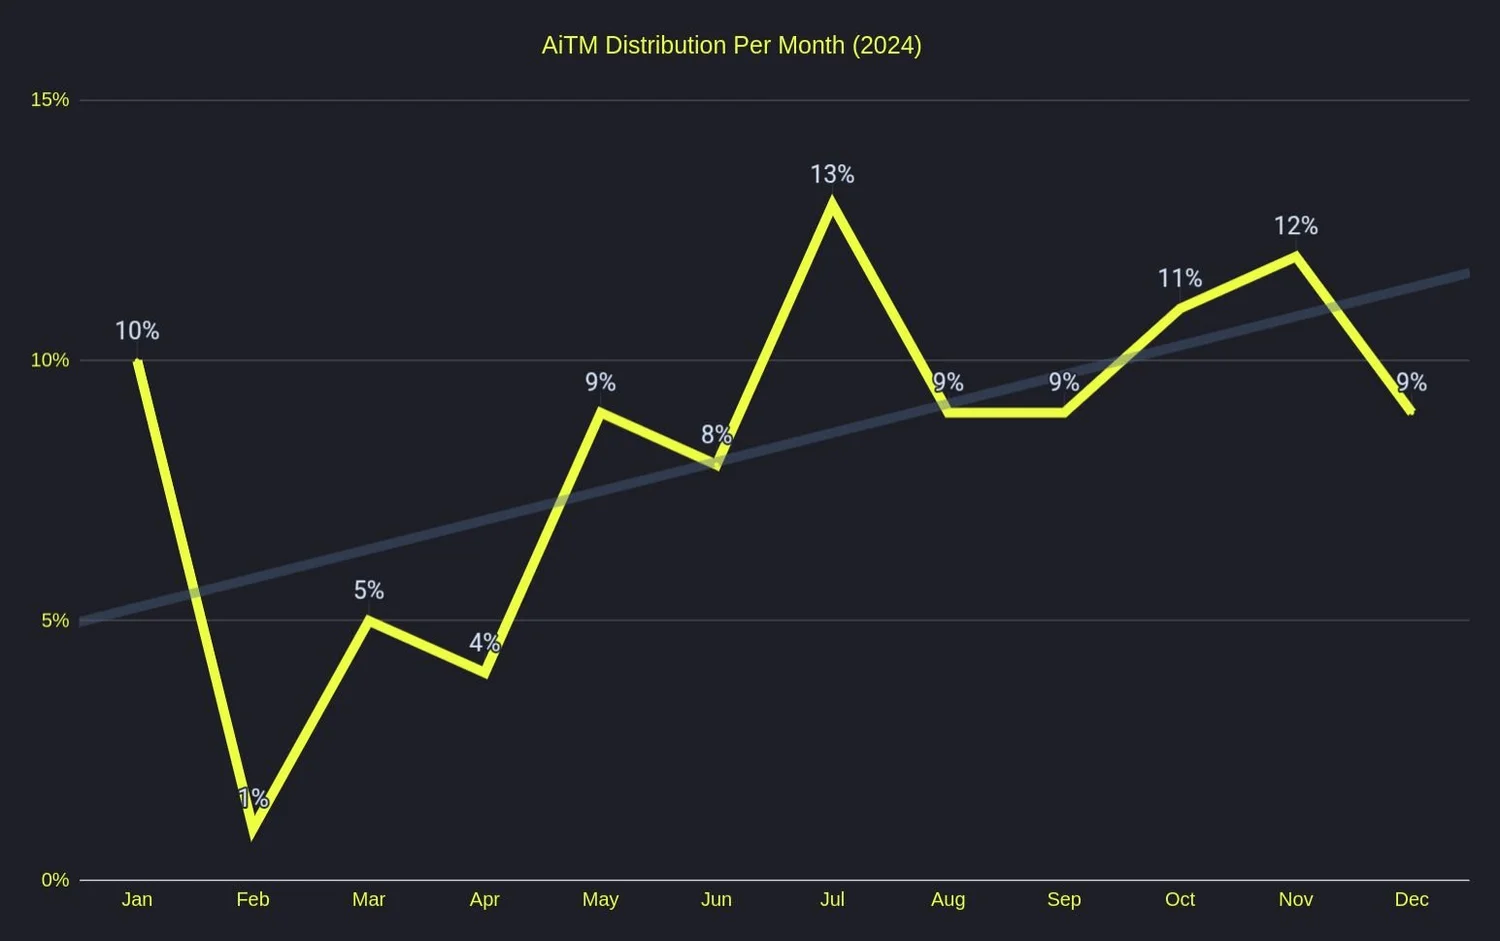
2024’s AiTM Activity In Numbers
Analysis of the AiTM infrastructure Lab539 tracked throughout 2024, including deployment timing, hosting choices and changing patterns.
Read research
File Hosting Services Used for Identity Phishing
A look at which legitimate file-hosting providers are most often impersonated in identity phishing campaigns.
Read research
Using Conditional Access Policies to Block Tor Exit Nodes in Entra ID
Using Microsoft Entra Conditional Access to deny authentication from Tor exit nodes.
Read research
A Summary of 6 Months Tracking AiTM Campaigns
Early observations from Lab539’s original research identifying AiTM backend infrastructure before operational use.
Read research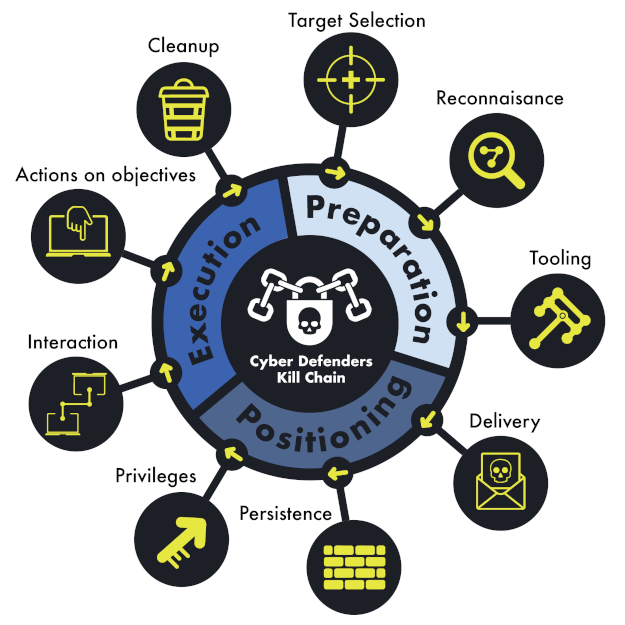
The Cyber Defenders Kill Chain (TCDO Part 2)
A defender-oriented view of the attack lifecycle and how it informs tailored cyber defence.
Read research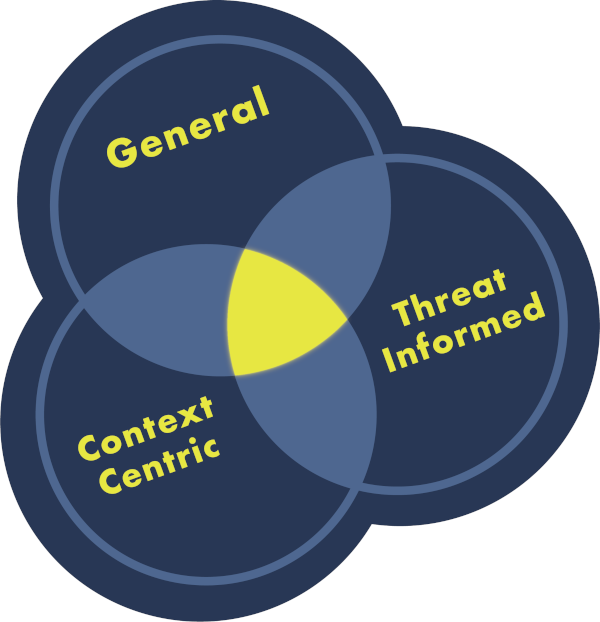
Applying Context, Controlling Adversaries (TCDO Part 1)
Why defensive context matters more than following adversary tradecraft in isolation.
Read research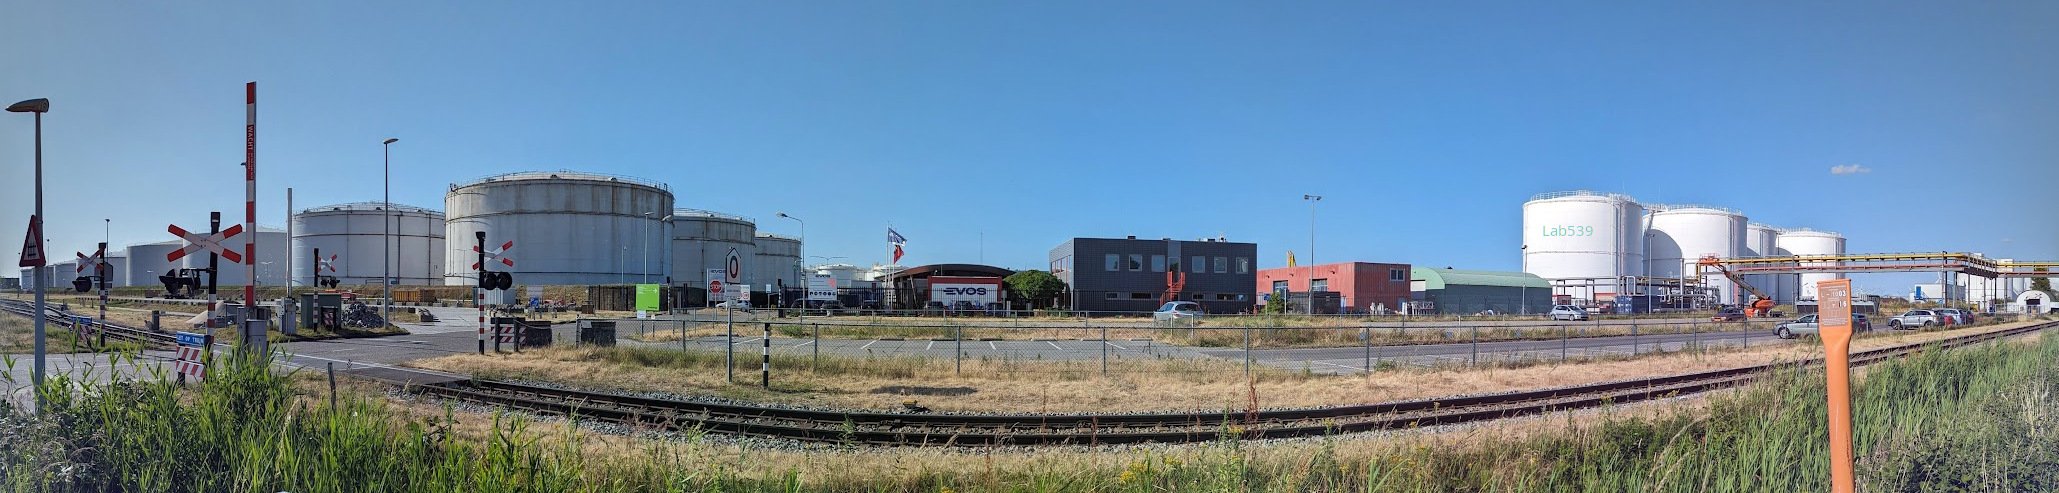
Cyber Security, Fuel Terminals and Operational Networks
The cyber threat to downstream oil and fuel terminals, and principles for protecting operational networks.
Read research
Inside Akira Ransomware Negotiations
Observations from Akira ransomware negotiations and what they reveal about adversary behaviour.
Read researchNo posts match those filters. Try another category or search.