Hunt AiTM infrastructure
We identify and track the infrastructure behind AiTM operations, including backend proxies that can persist as attackers change their domains and other disposable components.
We proactively hunt for the infrastructure behind AiTM attacks, often identifying it before attackers put it to use.
Our intelligence can be consumed as a feed or applied directly through existing security controls, including Microsoft Entra ID Conditional Access, to prevent authentication through known AiTM infrastructure.
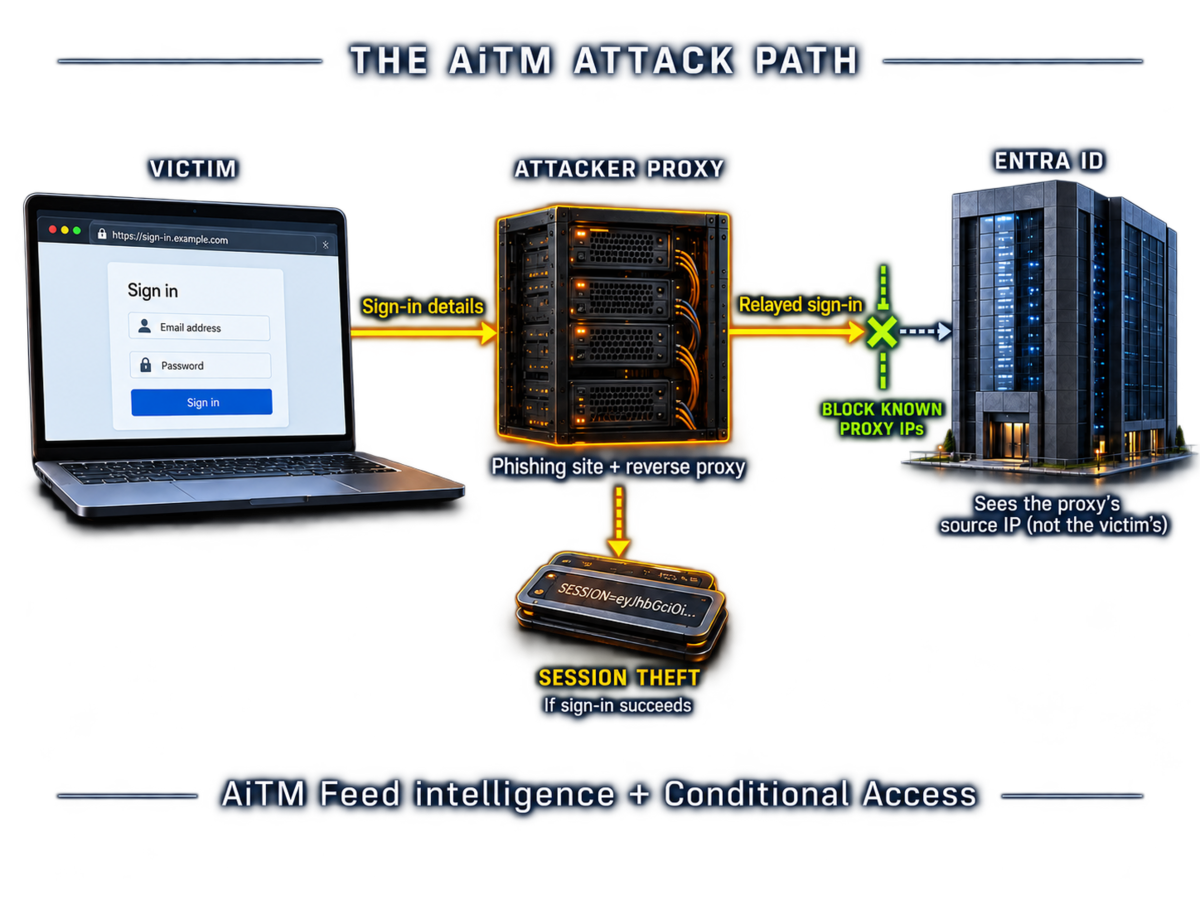
Adversary-in-the-Middle attacks rely on proxy infrastructure to intercept authentication flows and steal sessions. We proactively hunt that infrastructure, identifying the systems behind these attacks, often before they're used.
By integrating our intelligence directly into existing identity controls, we enable organisations to block authentication attempts originating from known AiTM infrastructure, preventing attackers from obtaining authenticated sessions.
We identify and track the infrastructure behind AiTM operations, including backend proxies that can persist as attackers change their domains and other disposable components.
Our Microsoft Entra ID integration keeps Named Locations updated with known AiTM infrastructure, enabling Conditional Access policies to reject authentication attempts originating from it.
Deploy our intelligence through Microsoft Entra ID, Microsoft Defender, APIs or standalone feeds. No additional endpoint agents or security platforms required.
A customer encountered active AiTM infrastructure, but an Entra Conditional Access policy rejected the authentication attempt using intelligence supplied by Lab539. Our published investigation traces the redirect chain, phishing frontend and underlying infrastructure.
Conditional Access / intelligence-backed policy
Documented in our July 2025 report ↗